The Bank of Ghana (BoG) is preparing to conduct thematic reviews of banks’ compliance with its revised Cyber and Information Security Directive as it steps up efforts to tackle digital fraud, cyber threats and other risks associated with the growing use of digital financial services.
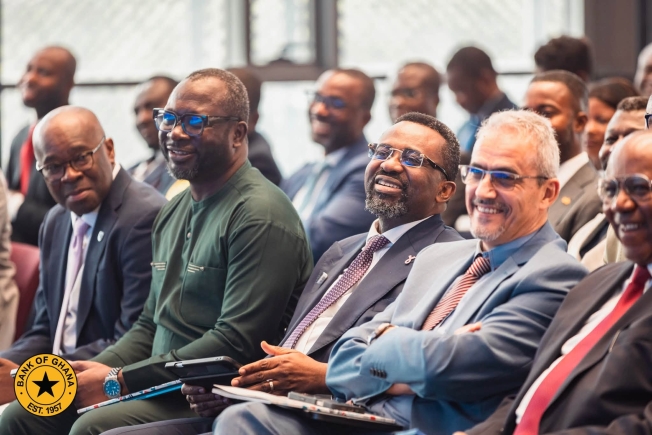
Governor of the Bank of Ghana, Dr Johnson Pandit Asiama, announced the planned reviews at the 43rd Annual General Meeting of the Ghana Association of Banks in Accra, highlighting the need for financial institutions to strengthen their cybersecurity measures and improve their resilience against emerging threats.
Here are the key reasons behind the planned reviews.
1. To Tackle Growing Digital Fraud and Cyber Threats
The increasing use of digital financial services has created new opportunities for fraudsters and cybercriminals to exploit vulnerabilities in banking systems. The BoG’s planned reviews are intended to assess how well banks comply with cybersecurity requirements and manage risks associated with digital transactions.
2. To Strengthen Compliance with Cybersecurity Regulations
The central bank intends to examine banks’ compliance with its revised Cyber and Information Security Directive. The reviews will help strengthen supervisory oversight and encourage financial institutions to implement the necessary measures to protect their systems, operations and customers.
Dr Asiama said the Bank had continued working with the Ghana Association of Banks and other industry players to facilitate the implementation of the revised directive.
3. To Protect Customer Data and Financial Information
Data protection is among the areas receiving increased supervisory attention. As banks handle growing volumes of sensitive customer information through digital platforms, effective safeguards are essential to reduce the risk of unauthorised access, data breaches and misuse of financial information.
4. To Address Risks Associated with Cloud Computing and Third-Party Services
Banks increasingly depend on technology providers and external service partners to support their operations. However, these relationships can introduce additional vulnerabilities.
The BoG has identified cloud computing and third-party dependencies as key areas of supervisory concern, signalling the importance of ensuring that banks adequately assess and manage risks arising from external technology services.
5. To Improve Banks’ Operational Resilience
Cyber incidents and technology disruptions can affect a bank’s ability to deliver essential services. The planned reviews will form part of broader efforts to ensure financial institutions can withstand, respond to and recover from operational disruptions.
Dr Asiama emphasised that cybersecurity and operational resilience must be treated as core business risks rather than matters solely for technology departments.
6. To Keep Banking Regulations in Step with Technology
The rapid evolution of digital financial services means that risks facing banks are also changing. The Governor stressed that regulatory and supervisory frameworks must evolve alongside technological developments and increasingly interconnected financial risks.
The reviews reflect the central bank’s focus on ensuring that its supervisory approach remains relevant to the changing banking environment.
7. To Build a More Resilient Banking Sector
Ultimately, the planned reviews are part of the BoG’s broader efforts to strengthen the resilience of financial institutions as digitalisation transforms Ghana’s banking industry.
Speaking at the meeting, Dr Asiama acknowledged that digitalisation has improved efficiency, convenience and financial inclusion, but warned that it has also created new channels through which risks can emerge.
The 43rd Annual General Meeting of the Ghana Association of Banks also featured the launch of the sixth edition of the GH Bankers’ Voice magazine.
Source: Ghana News Agency (GNA)

